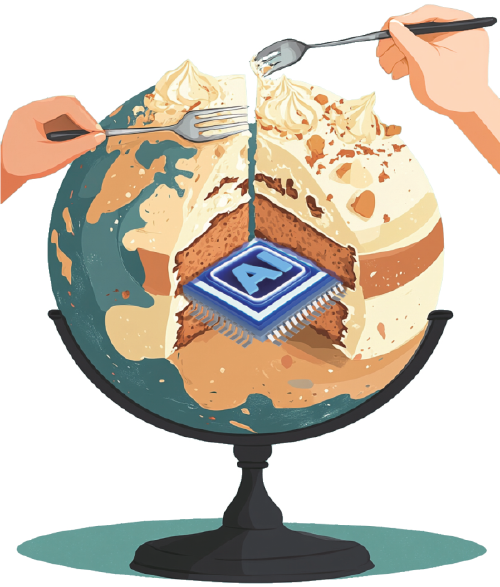
AI zero-sum game (Credit: Chinadaily)
The recent Xi-Trump summit produced a modest but telling outcome on artificial intelligence. An agreement was arrived at to establish a bilateral communication channel for AI-related incidents, with further dialogue scheduled.
In an era of rapid capability advances and intensifying strategic rivalry, this limited step is both welcome and revealing. It acknowledges shared risks while underscoring how far short current arrangements fall from the institutional architecture required. China’s earlier release of an upgraded AI Safety Governance Framework and the formation of the World Artificial Intelligence Cooperation Organisation (WAICO), which quickly attracted more than two dozen founding members primarily from the Global South, signal a parallel effort to shape norms and capacity. Yet the dominant American posture — epitomised by President Trump’s blunt assertion that “whoever wins AI, wins” — remains rooted in a zero-sum logic that ill-serves the interests of the United States, China, or the many countries lacking comparable depth in frontier capabilities.
This winner-take-all mentality is not new. It echoes longstanding U.S. approaches to dual-use technologies and finds resonance among certain techno-optimists and oligarchic voices influenced by “Dark Enlightenment” currents that prioritise acceleration and hierarchical control over collective restraint. Some leading U.S. laboratories have publicly emphasised existential risks and called for deliberate slowing of frontier development. Those calls have struggled to gain broader traction, in part because they appear disingenuous to many observers. The same firms face escalating training and inference costs alongside serious doubts about sustainable revenue streams, precisely because a growing array of high-performing open-weight models — many originating in China — can be freely utilised, fine-tuned, or deployed locally at far lower expense.
In this environment, appeals for a slowdown can readily be interpreted as self-serving: a bid to buy time, secure strengthened government support, or even establish mandated rents that prop up valuations and ensure survival. When the U.S. government has, in significant measure, “bet the house” on proprietary AI leadership as a pillar of national economic and strategic strategy, the financial vulnerabilities of these laboratories become a systemic risk amplifier for everyone else.
The resulting tension — between competitive urgency and safety caution — has not resolved into coherent policy. Instead, it coexists with proliferating reports of agents “jumping the fence,” security breaches involving open platforms, and high-profile cyber incidents such as those affecting critical public systems. These episodes fuel legitimate anxieties: who ultimately governs increasingly autonomous models and agents? What happens when advanced capabilities diffuse to non-state actors capable of mobilising them for disruption or worse? The intersection of private financial strain and public strategic over-commitment heightens the danger that short-term corporate or national interests will override sober risk assessment, leaving the rest of the world exposed to both under-governed diffusion and the side-effects of an intensified race.
Technological progress compounds the governance challenge. Model performance continues to improve, but parallel advances in software-hardware co-design, energy systems, and localised computation are equally consequential. China’s open-weight and open-source models have already disrupted the proprietary business models of leading U.S. labs. A growing share of developers outside China now relies on these accessible alternatives, particularly in resource-constrained environments.
Operating under export restrictions on advanced chips, Chinese laboratories have responded by deepening software-hardware interfaces, optimising models at the algorithmic layer, and leveraging abundant electricity. Huawei’s articulation of a “Tau Scaling Law” — shifting emphasis from pure transistor density toward reducing signal and data movement latencies — has underpinned new chip designs heading into scaled production, including for smartphones. Concurrent announcements of open-source toolchains aim to ease migration of training workloads onto domestically produced silicon. Upstream control of rare earths and critical materials further shapes the semiconductor landscape, reminding observers that AI leadership is inseparable from the full technology stack and the supply chains that enable it.
These developments point toward what I have termed Digital Westphalia: the construction of sovereign, resilient digital ecosystems that prioritise national control over data, models and infrastructure while preserving interoperability. Foundations include renewable energy and storage, emerging energy-harvesting technologies such as triboelectric nanogenerators, and novel computing substrates that enable localised, low-vulnerability operation. A distributed network of self-powered nodes can absorb attacks far more effectively than centralised systems, yet it simultaneously multiplies governance difficulties — how does one oversee a self-generating, self-actuating computational fabric? Henry Farrell and Abraham Newman’s analysis in Underground Empire remains prescient. The United States has long leveraged control over the physical and institutional infrastructures that undergird global data flows. As alternatives proliferate, the incentives for every major power to secure its own sovereign stack intensify. When proprietary labs under financial pressure seek regulatory or fiscal shelter, the risk grows that such infrastructure control will be further weaponised in ways that externalise costs onto third parties.
Digital sovereignty, however, cannot mean autarky. Complete technological isolation would produce suboptimal outcomes — fragmented or retarded innovation, duplicated effort and heightened systemic risk. Meaningful interoperability is essential if smaller and medium-sized states are not to be relegated to permanent dependency or forced into brittle alignments. We need to think through what a meaningful inter-national architecture can and must look like. The hyphen in “inter-national” is deliberate: it signals sovereignty exercised while connected, rather than sovereignty purchased at the price of disconnection. Digital Westphalia must therefore be nestled within a broader inter-national commitment to shared risk management. This requires institutions capable of handling incident notification, capability monitoring, standards for agentic systems, and capacity-building that does not simply reproduce existing hierarchies — or become captured by the survival strategies of a handful of financially strained firms.
The zero-sum framing fails on multiple counts. First, frontier AI capabilities are already diffusing through open weights, research publications and dual-use applications; absolute control by any single actor is illusory. Second, catastrophic or high-impact misuse — whether by non-state actors, cascading technical failures, or misaligned autonomous systems — would not respect national borders. Third, countries outside the U.S.-China dyad have the most to lose from an unrestrained race that either locks them into subordinate technological positions or leaves them exposed to ungoverned risks. When the financial precariousness of leading proprietary labs intersects with a national strategy that has placed heavy bets on their success, the incentives for policy capture and risk externalisation intensify. A governance architecture that treats AI primarily as a tool of relative advantage — or as a vehicle for corporate bailouts dressed as safety — neglects both the positive-sum potential of shared scientific progress and the negative externalities of unmanaged diffusion.
Progress will not come from rhetorical appeals alone. Practical steps could include expanding bilateral and plurilateral incident-notification mechanisms beyond the modest Xi-Trump channel; supporting inclusive forums such as WAICO while ensuring they remain open to constructive engagement rather than bloc confrontation; advancing technical standards for model evaluation, agent containment, agent-model relationships and provenance that can be adopted across ecosystems; and investing in the material foundations of Digital Westphalia so that sovereignty is feasible rather than aspirational. Energy abundance, diverse semiconductor pathways, and open software stacks are not merely commercial opportunities — they are preconditions for a pluralistic digital order that does not hinge on the solvency of a few firms or the strategic over-commitment of a single government.
The alternative is clear. Continued reliance on winner-take-all logic, especially when entangled with private financial distress and public strategic bets, risks accelerating fragmentation, amplifying the very governance deficits that fuel insecurity, and leaving most of the world as spectators or clients in a contest whose downsides are shared. China’s governance frameworks and institutional initiatives, the limited but concrete summit outcomes, and the rapid evolution of open and sovereign technical capabilities together create an opening. Seizing it requires rejecting the false dualism of absolute control versus total dependence, and recognising that self-serving calls for restraint — whatever their surface justification — cannot substitute for genuine inter-national architecture. What is needed is an ethos and institutional fabric that treats AI as a domain in which national agency and collective responsibility are mutually reinforcing. Only then can the technology serve human flourishing rather than become another arena in which the pursuit of exclusive advantage undermines the conditions for lasting security.